DarkSword router's iOS 26 route, C10, is switched off
An iPhone exploit server we captured on 4 and 5 November 2026 picks Coruna or DarkSword by iOS version. It keeps a third route, C10, for iOS 26. A config file has C10 switched off, nothing is deployed at its path, and its only iOS 26 plugin is filed under a Google Chrome CVE.
| Server | 154.222.16[.]220 |
|---|---|
| Router | /client/chain/ios_chain_routing.js |
| SHA-256 | 7cb1f1eb8a181b4c25e1c6308498361c604edc91466522848cc29f954fa10429 |
| Captured | 4 November 2026 at 16:05:33 UTC, files read again on 5 November |
| C10 switch | /profiles/c10_deploy.json, enabled: false |
Update (6 November 2026, 16:00 UTC): C10 was staged on two Cloudflare Pages sites in August and September 2026 with generated iOS 26 offsets, and was gone by November. The same router runs on 72 sites and names its builder on Telegram. See C10 was staged on Cloudflare Pages and The router names its builder.
Update (6 November 2026, 10:30 UTC): Two Chinese source-code markets sell the kit as "Caishen iOS C2 V2", with Coruna, DarkSword and C10 listed as its three chains. See The kit is for sale.
Key takeaways
- An iPhone exploit server at 154.222.16[.]220 routes visitors by iOS version. iOS 13 to 17 gets Coruna, iOS 18 gets DarkSword, and anything newer goes to a route called C10.
- C10 is controlled by one JSON file,
/profiles/c10_deploy.json. On 5 November 2026 it read"enabled": false, and the server had no files at the C10 path. In August and September a full C10 tree sat on two Cloudflare Pages sites, built on offsets with placeholder hashes. - The server lists one exploit plugin for iOS 26, filed as CVE-2026-10001. That CVE is a Google Chrome bug, and the plugin's gadget addresses are
0xFFFFFFF007123456and0xFFFFFFF007234568. - Visitors land on a fake Cloudflare check branded for OKX. When DarkSword fails on a phone, the loader falls back to Coruna, and both kits report to the same server.
- The kit is sold on Chinese source-code markets as "Caishen iOS C2 V2". Its landing-page router ran on 72 sites from 4 October to 5 November 2026, on domains that copy WhatsApp, Coupang, Hepsiburada and Mizuho Bank, and names its builder as Telegram
@caishenge.
Acknowledgements: Aidan Holland of Censys documented the gooll chain on hdios[.]cn and an unfinished iOS 26 chain in the DarkSword/Coruna Open Directory Finding Report on 7 October 2026.
This server has a route for iOS 26, and the route is switched off. We captured its landing page on 4 November 2026. On 5 November we requested its config, router and chain files by path.
Background
Coruna and DarkSword are iPhone exploit kits disclosed in March 2026. Coruna covers iOS 13 to 17.2.1. DarkSword, described by Google, iVerify and Lookout, covers iOS 18.4 to 18.7.
DarkSword's code leaked days after disclosure. Other operators have served it since.
Apple named the release after iOS 18 "iOS 26". There was no iOS 19 to 25, so a route for "iOS 19 and later" is a route for iOS 26.
In October, Censys found an operator's working files in an open directory. They included a gooll/ chain on hdios[.]cn and an iOS 26 chain whose later stages were one-byte placeholders. The server in this article has the same client/, profiles/ and gooll/ folders.
Infrastructure
The IP was reported publicly as a ClickFix host at 15:30:13 UTC on 4 November 2026. We captured it 35 minutes later. It shows a fake Cloudflare check, which explains the ClickFix label, but the page copies no command. It loads an iOS router.
| Time (UTC) | Event |
|---|---|
| 2026-08-22 | A C10 tree for iOS 26 is served from fk-94e.pages[.]dev |
| 2026-09-12 | A newer C10 tree is served from zdjz.pages[.]dev |
| 2026-10-04 | First public scan of the Caishen router, on www.caik[.]my |
| 2026-10-07 | Censys publishes its report on the operator's open directory [Censys] |
| 2026-10-22 | First router build that sends iOS 19 and later to C10 |
| 2026-10-31 15:36:12 | Last update to the server's iOS 18.7 allowlist, per its updated_at field |
| 2026-11-04 15:30:13 | 154.222.16[.]220 reported publicly as a ClickFix host |
| 2026-11-04 16:05:33 | Our capture of the landing page and the router |
| 2026-11-04 | jumahub[.]com lists the kit for 388 USDT |
| 2026-11-05 | /profiles/c10_deploy.json reads "enabled": false; lab page and plugin list read |
| 2026-11-06 | /C10/b.html returns 404 on both Pages sites and on five router hosts |
The server answers any path it does not have with its landing page. That page is 18,187 bytes, SHA-256 24bf40a618f164223b7e8d32b3f7fc4f9110b4c304189306790d39355f0901f3. The server returns it for /favicon.ico, /C10/ and /C10/b.html.
Technical analysis
Stage 1: A fake Cloudflare check branded for OKX
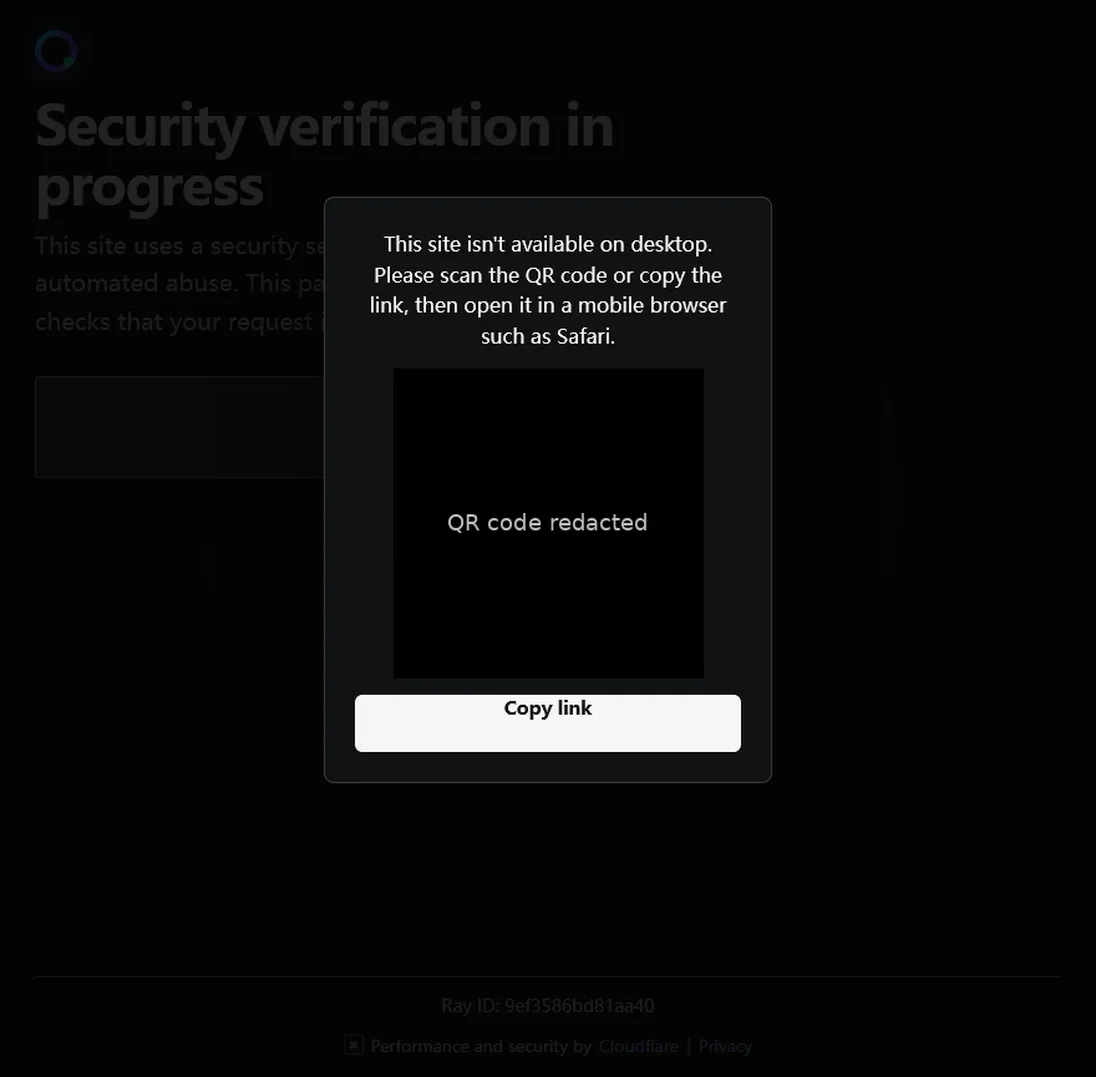
The landing page copies Cloudflare's "Security verification in progress" screen, down to a Ray ID. Its settings file, /src/recaptcha.config.js, sets siteDomain to OKX and redirectUrl to https://web3.okx.com/.
The page wants an iPhone in Safari. A desktop visitor gets a QR code to scan with a phone. A phone in another browser is told to open the page in Safari.
When a chain reports back, the page switches to "Verification complete". It tells the visitor to keep Safari open with the screen on for about two minutes. The script holds back the OKX redirect so the visitor stays on the page.
Stage 2: The router picks a chain by iOS version
The landing page loads /client/chain/ios_chain_routing.js and /client/lp-router.js. A comment at the top of the routing module says the operator's panel, API and landing page all share it.
The router reads the iOS version from the browser. It fetches two JSON files from /profiles/. Then it opens the chosen chain in a hidden frame, 1 pixel wide at 0.01 opacity.
The landing page turns on an automatic lab mode. That sends iOS 18.6.3 and later to the lab page with no lab flag in the link. For iOS 18.7, the router moves the whole tab there. A comment in lp-router.js says Safari throttles the hidden frame and the stages never start.
The server also keeps an iOS 18.7 allowlist, /profiles/ios_187_gray_gate.json. It holds one device: build 22H311, iOS 18.7.5, with a serial number.
The lab page starts the DarkSword stages with rce_loader.js. If the first stage fails, the loader logs a fallback to Coruna. The same page carries a token for posting Coruna results, so both kits report to one panel.
Stage 3: The C10 route is a switch in a JSON file
Every visitor on iOS 19 or later goes through this function:
function c10DeployActive(c10Deploy, ios, ctx) {
  if (!ios || typeof ios.major !== 'number') return false;
  const lab = !!(ctx && ctx.lab);
  const force = !!(ctx && ctx.forceC10);
  const min = c10Deploy ? Number(c10Deploy.min_ios_major) || 19 : 19;
  if (ios.major < min) return false;
  if (c10Deploy && c10Deploy.enabled) {
    if (c10Deploy.lab_requires_flag && !lab) return false;
    return true;
  }
  return lab && force;
}
C10 opens in two cases: the config sets enabled, or the link carries the test flags ?lab=1&c10=1. On 5 November the config read "enabled": false, "min_ios_major": 19 and "c10_path": "/C10/b.html".
The config's notes are in Chinese. They say that once enabled, iOS 19 and later goes to /C10/b.html, apart from the iOS 18.7 DarkSword line. The C10 secret is kept on the server.
With C10 off, the router logs a status for the panel: "not supported (C10 not mounted in production)". A banner script holds the text for the same case: "iOS 19+ is outside the 13 to 18.7 coverage promise; while C10 is off, visit only."
The C10 path has nothing behind it. /C10/b.html returns the landing page. Its scripts load from under /C10/, and every one returns 404, as does /C10/root.js, the file the config notes name.
C10 was staged on Cloudflare Pages
The C10 files did exist, on two Cloudflare Pages sites. Public scans show fk-94e.pages[.]dev/C10/b.html on 22 August and 9 September 2026, and zdjz.pages[.]dev/C10/b.html on 12 September. Each loaded /C10/root.js and dozens of scripts from /C10/client/ and /C10/chains/.
A version router, ios26_version_router.js, covers iOS 26.0 to 26.3. Its stages are named for CVE-2025-43529 and CVE-2025-14174, fixed in December 2025, and CVE-2026-20700, fixed in February 2026. Apple said all three were used in the same attacks. For iOS 26.2 and 26.3 it lists Coruna as the browser stage.
The chain needs memory offsets for each iOS build, and its offset profiles are generated. The 26.5 and 26.6.1 profiles give the cache hash as 64 zeros and the file size as 0. One 26.0 profile gives the hash as a1b2c3d4e5f6a7b8, and another says its symbols are "NOT from a real dyld_shared_cache".
The comment at the top of root.js calls the code "competitor JS" moved under /C10/. It sends logs to mkl3[.]xyz/api/log and names k68k[.]xyz as its C2. Both domains were registered through NameSilo, on 18 and 20 June 2026.
On 6 November both Pages sites returned 404 for /C10/b.html.
The iOS 26 plugin carries a Chrome CVE
The DarkSword lab page loads /api/plugins/list. It lists four exploit plugins, each with an iOS range, a priority and a reliability score:
| Plugin ID | iOS range in the list | What the CVE record says |
|---|---|---|
| CVE-2025-24243 | 17.0 to 18.4.1 | Apple, fixed in iOS 18.4 |
| CVE-2025-31203 | 18.0 to 18.5 | Apple, fixed in iOS 18.4 |
| CVE-2025-31250 | 18.4 to 18.7.2 | Apple macOS only, fixed in macOS Sequoia 15.5 |
| CVE-2026-10001 | 26.0 to 26.3 | Google Chrome, fixed in 148.0.7778.216 |
The list calls CVE-2025-31250 a bug in how iOS parses HEVC video. Its CVE record is a macOS privacy fix, with no iOS release listed.
CVE-2026-10001 is the only plugin for iOS 26. The list gives it the top priority, 9, and a reliability of 0.75. Its CVE record is a use-after-free in Google Chrome, published on 28 May 2026.
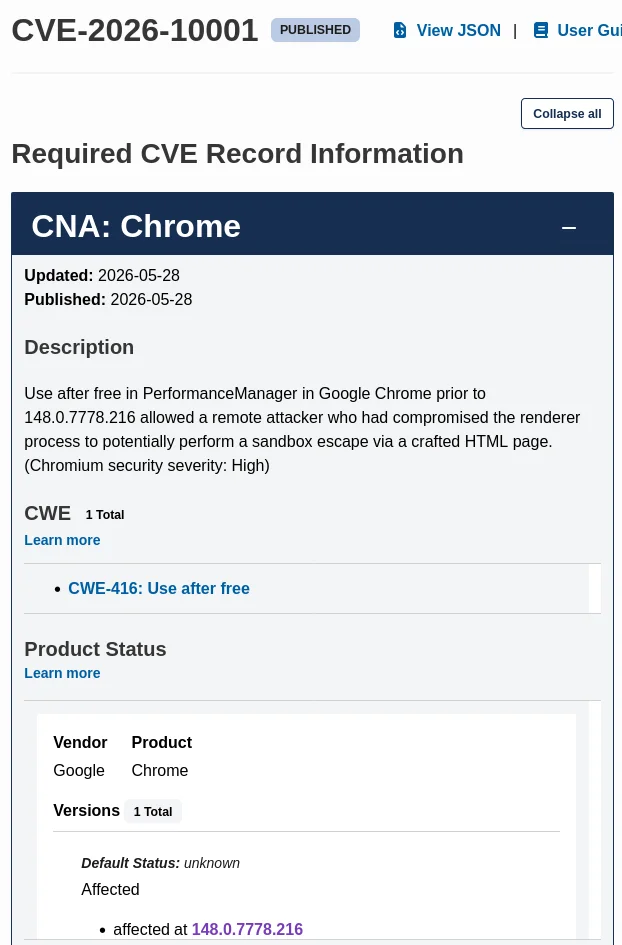
The plugin file, /plugins/CVE-2026-10001/exploit.js, calls itself a dyld4 hijack "specific to iOS 26". Its default gadget addresses end in counting digits:
    pivot_gadget: 0xFFFFFFF007123456,
    jop_dispatch: 0xFFFFFFF007234568,
The plugin needs a memory read and write from an earlier stage. The server's browser stages stop at iOS 18.
The kit is for sale
Two Chinese source-code markets sell the kit under the name "Caishen iOS C2 V2". Caishen is the Chinese god of wealth.
The listing on 022zxyy[.]com names three chains, Coruna, DarkSword and C10, covering iOS 13 to 19. It describes a Python FastAPI backend, a Vben Admin panel and collection of TRX, ETH and BTC wallet balances. Its page counted 5 sales when we read it on 6 November.
The listing on jumahub[.]com, posted on 4 November, sells an iOS exploit panel with a landing page for iOS 13 to 18.7. It costs 388 USDT and carries the same Caishen iOS C2 V2 tag.
Two details match this server. C10 is the name its router gives the iOS 26 route. Its banner text promises coverage of iOS 13 to 18.7, the range jumahub sells. The seller lists C10 as a working chain, and on this server it was switched off with nothing behind it.
The router names its builder
The same kit has a lighter router, lp-router.js. Its first public scan was on www.caik[.]my on 4 October 2026. The comment at its top lists the routes: iOS 13 to 17 to Coruna, iOS 18 to "DarkSword PE", iOS 19 and later "not loaded". The last line, translated, reads "Setup, custom development, site maintenance: Telegram @caishenge".
Public scans from 4 October to 5 November show 72 sites loading 17 builds of this router from about 17 hosts. Some builds keep @caishenge. Others carry @qqdata_ops, @rmb132, an empty handle or the words "iOS V2 management system". Their domains copy WhatsApp, the shopping sites Coupang and Hepsiburada, and Mizuho Bank.
Builds from 22 October on add a C10 line: "iOS 19+ -> C10 (caik /C10/b.html)". On 6 November that path returned 404 on the five router hosts we checked.
The OKX-branded settings file from this server, /src/recaptcha.config.js, is byte-identical on about 100 hosts scanned since 17 October. Seven of them share 203.91.72[.]250 and serve the same gooll.html.
Impact
Exposure: every visitor on iOS 13 to 18.7 who reaches the landing page is routed to Coruna or DarkSword stages. A visitor on iOS 26 gets the fake check, and the router logs the visit and loads no chain.
The OKX lure ran on about 100 hosts and the router on 72 sites between 4 October and 6 November 2026.
The router fetches /profiles/c10_deploy.json fresh on every visit. A change to that file applies from the next page load.
Indicators of compromise (IOCs)
Network indicators
| Indicator | Context |
|---|---|
154.222.16[.]220 |
Landing page, router, chain stages and logging |
hxxps://154.222.16[.]220/profiles/c10_deploy.json |
C10 switch |
hxxps://154.222.16[.]220/profiles/ios_187_gray_gate.json |
iOS 18.7 allowlist |
hxxps://154.222.16[.]220/gooll/gooll.html |
DarkSword production page |
hxxps://154.222.16[.]220/gooll/lab_187.html |
DarkSword lab page for iOS 18.6.3 to 18.7 |
hxxps://154.222.16[.]220/api/plugins/list |
Plugin list |
hxxps://154.222.16[.]220/logs?id=-1&text=lp-router |
Router logging |
203.91.72[.]250 |
Seven gooll landing domains |
hxxps://www.caik[.]my/js/lp-router.js |
Caishen router, Telegram @caishenge |
hxxps://fk-94e.pages[.]dev/C10/b.html |
C10 tree, August and September 2026 |
hxxps://zdjz.pages[.]dev/C10/b.html |
C10 tree, September 2026 |
mkl3[.]xyz |
C10 logging, /api/log |
k68k[.]xyz |
C10 C2 |
hxxps://www.022zxyy[.]com/39455.html |
Sale listing for the kit, Caishen iOS C2 V2 |
hxxps://www.jumahub[.]com/944.html |
Sale listing for the kit, 388 USDT |
File hashes (SHA-256)
| SHA-256 | File |
|---|---|
24bf40a618f164223b7e8d32b3f7fc4f9110b4c304189306790d39355f0901f3 |
Landing page, also served at /C10/b.html |
7cb1f1eb8a181b4c25e1c6308498361c604edc91466522848cc29f954fa10429 |
/client/chain/ios_chain_routing.js |
3c4e1d343a98b45e2dc405760b6582178d6c646a67e3ae1bf582e29638a21ff0 |
/client/lp-router.js |
fda9ab968518d9e1cb50af5582a94dc0bb444320c0c302260d957a22dbf89756 |
/client/chain_status_banner.js |
0f7db28dd72dca3a2964d30ff7b4f28cd97016fb6a738c8a7c58bbe5896a9cfb |
/src/recaptcha.config.js |
1d3734079bc317dbf56f5c8eba3e532f85ea7d55f4c53da4b3db979ded62d961 |
/src/recaptcha.js |
cb6671cfb92db0a321a23667b4250b5774283ac042a3e42a3d768315b4778d11 |
/profiles/c10_deploy.json |
0d7aea9d04dbc98f8bbb3f3c9c754f1fecff2b78be276b5a790b0c7bdbe2230f |
/profiles/ios_187_gray_gate.json |
349a2aa3510e01bcfe9662d6df4a61673b0b94008dd620ec88717bfe4d9d0bbf |
/api/plugins/list |
9259130c2ecbcf754bc7dd1ba8dedf0f74c612396032f89df43b562fd44e1856 |
/plugins/CVE-2026-10001/exploit.js |
64ef647cdf099c39b0482a2cbe5137674068d623a8906e25666db93e059d2401 |
/plugins/CVE-2025-31250/exploit.js |
83a06c02d0d09a672d027a0067e1c59c995b27ac56539f662ed451a78d8720ef |
/gooll/gooll.html |
cc6538afe5dd755854fe9f853241b6c0fcffcc9e183468261f42b24666b4d7de |
/gooll/lab_187.html |
db7ec0a17ca52d28ceed5351902e39e48bf3a0ae335c7a1803b51960d7287559 |
/gooll/rce_loader.js |
9d3a355c1e21bcc9fc62811ef70916e0d15247542e45bbf5fd5f125950e34b34 |
Caishen lp-router.js on www.caik[.]my |
07238b2b19c197694b911fe35ae7142ea773e20c75138fb7a52fd51f710b509e |
Caishen lp-router.js build with the C10 route |
3fc1292afde911fd4acf94cc178eee57a3f14828768de94bf725e4cc3f5f244c |
/C10/root.js on zdjz.pages[.]dev |
4926fe16bd8463565e023adcc87cd65b43ce0b8d223e7ad4f9e8d42f86b36b35 |
/C10/root.js on fk-94e.pages[.]dev |
b8a5fbf22d70e17f8bfd3dff50b3858962f83851656cfe7ee2c19505e5dd9e87 |
/C10/client/ios26_version_router.js |
About the author
Matt Kirkland (Kirk) is the founder of Ohey and researches malware, compromised websites and the infrastructure behind them.
More reading
 KongTuke ClickFix comes for a Canadian treasure: Canada Dry
 ClockTail: a ClickFix kit that never filled in its command
 Polymarket wallet drainer served from DebugBear's script CDNCoruna: hidden website frames and an iOS exploit dispatcherDarkSword: the iOS 18 exploit kit, its gates and iOS 26iOS exploit kits on websites: hidden frames and loaders